Sovereign security for SMEs
From log noise,
to incident response.
Harold reads your application logs, flags suspicious activity, groups related alerts into incidents, and shows your team the evidence for a response.
The problem for SMEs
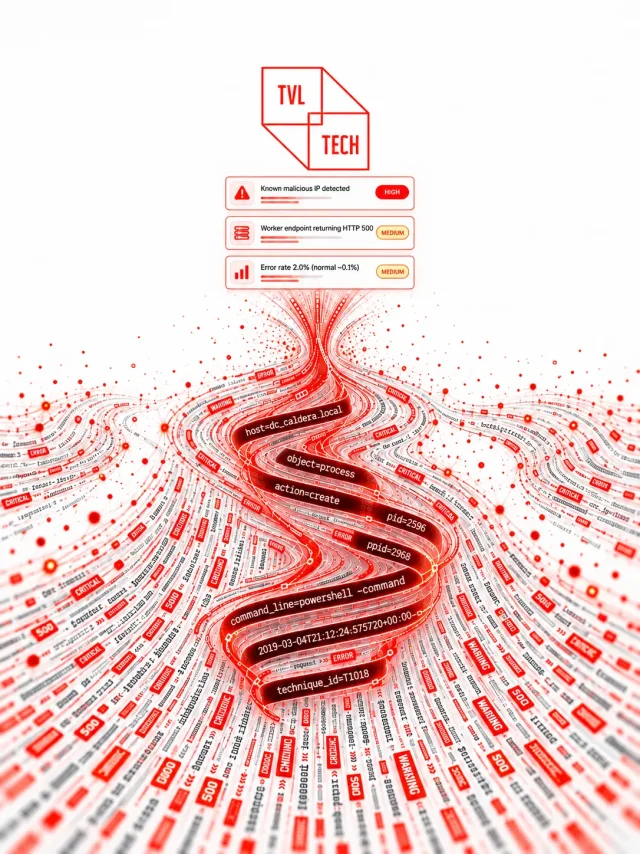
Attacks scale.
Small teams cannot.
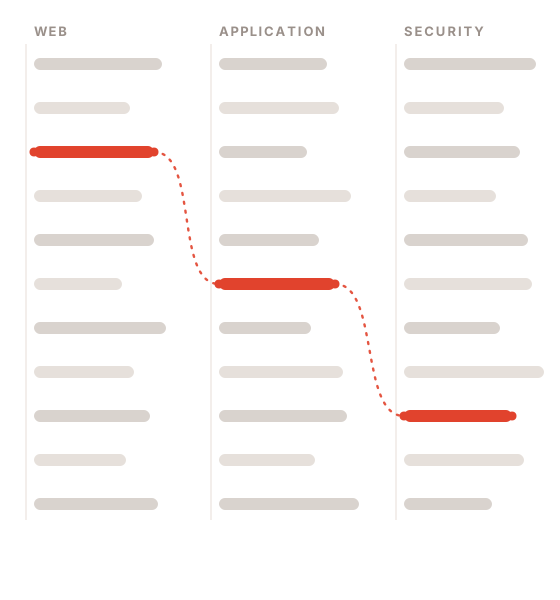
As threats accelerate, web logs, application errors and security alerts arrive in separate streams. A small team has to connect them before it can respond.
Sources: UK NCSC · ENISA — SMEs Cybersecurity
One 24-hour deployment
A day of logs.
A focused review queue.
Harold deduplicates, detects, groups and enriches — so a day of raw telemetry becomes a short list a person can actually work.
connected sources
raw log lines read
incidents to examine
Supported source types
SOC · Authentication
Failed logins.
Then admin access.
Eight addresses try one account. A later login succeeds, then the session touches an admin route.
AI only when needed.
One account · 8 source IPs · 12 minutes
Match the pattern
A local sequence check counts failures for the account across IPs.
See what followed
A new-IP login succeeds; the session requests /admin/users.
Open one incident
Failures, login and route events stay together. No model call for the initial detection.
NOC · Application performance
Checkout slows.
Find the cause.
Query logs, database pressure and failed requests point to one issue your team can investigate.
Assign the application owner. Check the query and connection pool, then verify latency after the fix.
Query slows
Slow-query log on /checkout
Connections wait
Database pool wait starts to rise
Responses lag
Checkout p95: 180 ms → 2.4 s
Requests fail
HTTP 500 appears · 42 requests affected
Human-approved response
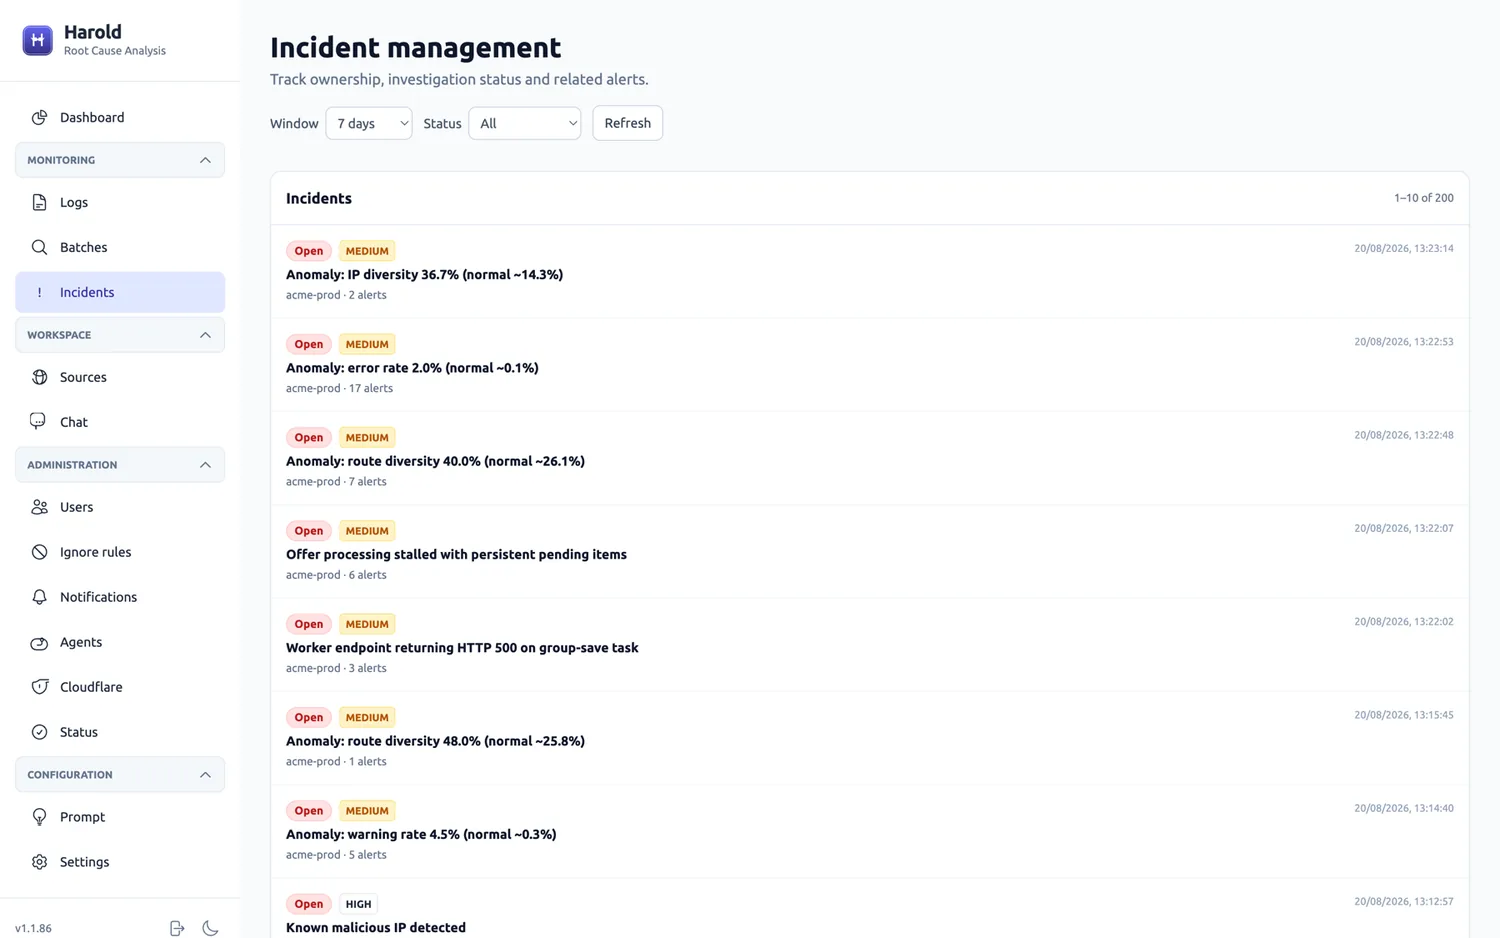
See the evidence.
Stay in control.
Harold recommends what to examine. Your team makes the decisions that affect production.
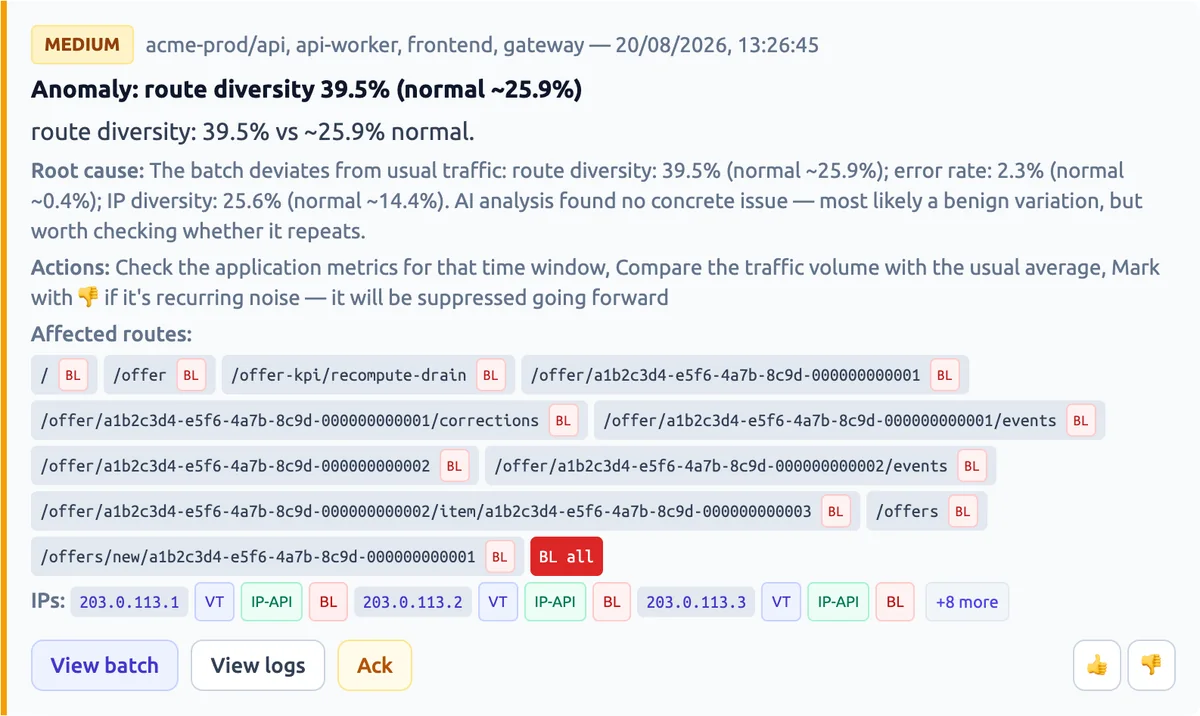
See why it was raised
Inspect source events and related signals before recording a verdict.
Approve any edge block
A Cloudflare block requires a separate operator action.
Choose where data goes
Run in your environment with local or hosted model analysis.
Tune recurring noise with scoped exceptions and replay before rollout.
Pricing
€100 a month.
Up to a million alerts.
Pricing counts processed alerts, not raw log lines — so the bill tracks what reaches a verdict, not your traffic volume.
Up to one million alerts processed per month.
The whole pipeline runs on your own infrastructure, with a locally hosted model when log content must not leave the perimeter. Pricing counts processed alerts; the deployment figures above count raw log lines.
See it for yourself
See Harold
work live.
Bring one application and a sample of its logs. In a 30-minute demo, follow a finding from log line to incident and discuss a pilot on your data.